Blog
Field notes
Mobile security, written for the people who fix it.
Featured
Mobile App Security Compliance Guide: PCI DSS, HIPAA, GDPR, SOC 2, and More
Which security and privacy rules apply to your mobile app, and what do they actually require? A plain-language guide to PCI DSS, HIPAA, GDPR, SOC 2, India’s DPDP Act, and app store privacy rules.
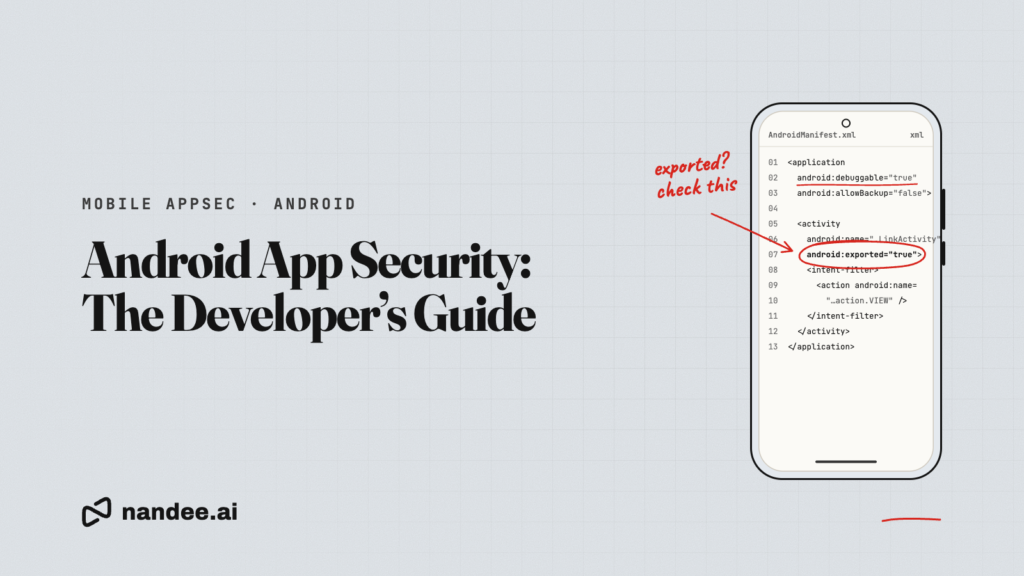
Android App Security: The Developer’s Guide
A practical guide to securing Android apps: storage, networking, the manifest, components, WebViews, deep links, dependencies, and release builds, with code you can use today.
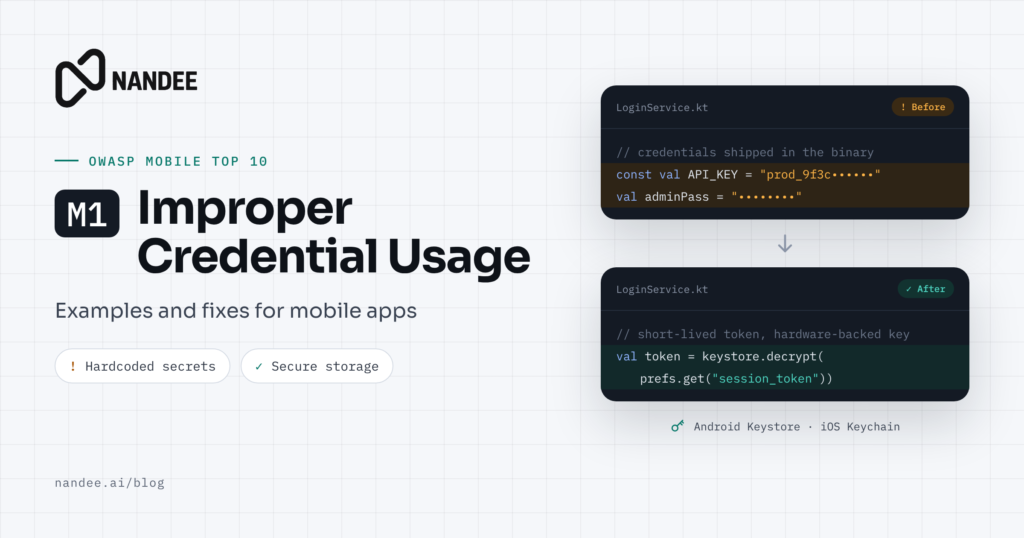
M1 Improper Credential Usage: Examples and Fixes for Mobile Apps
Improper credential usage is number one on the OWASP Mobile Top 10 (2024). Learn what it looks like in Android and iOS apps, why it happens, and the fixes that keep API keys and tokens out of attackers’ hands.
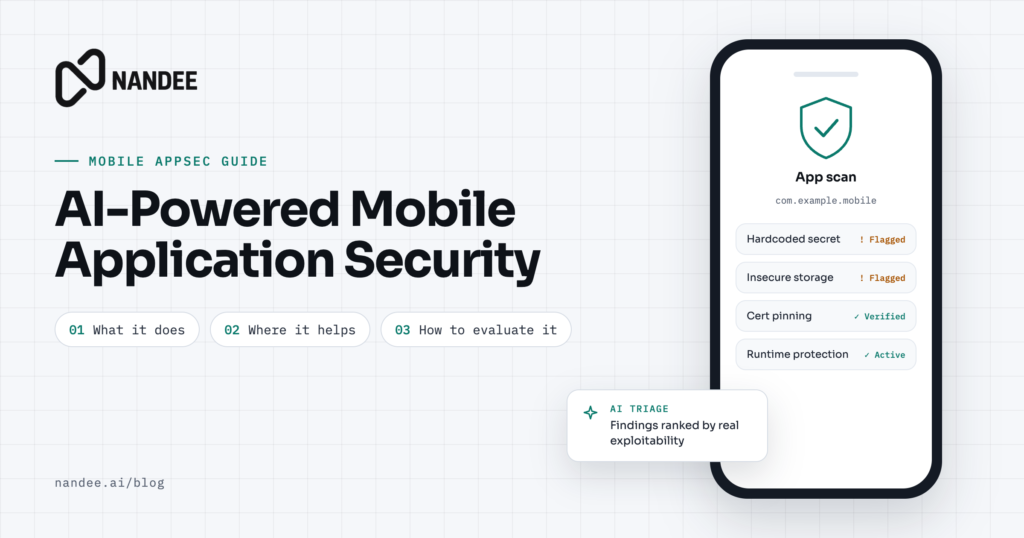
AI-Powered Mobile Application Security: What It Does, Where It Helps, and How to Evaluate It
AI is changing how mobile app security findings are detected, triaged, and fixed. Here is what AI-powered mobile security actually does well, where it still needs a human, and how to judge a tool before you buy.
OWASP Mobile Top 10 (2024): A Complete Guide for Developers
The OWASP Mobile Top 10 (2024) explained for developers: what each of the ten risks looks like in a real Android or iOS app, how to fix it, and how to test for it.
What is Mobile Application Security? A Complete Guide for 2026
What is Mobile Application Security? A Complete Guide for 2026 Mobile applications have become the primary gateway between users and digital services. From banking and healthcare to social…